Why Sessions Break in Laravel — Understanding What Actually Happens Behind the Scenes
Laravel sessions often feel simple when everything works correctly. A user logs in, Laravel remembers who they are, form validation errors survive a redirect, flash messages appear on the next page, and CSRF protection quietly protects forms in the background. Because Laravel handles so much of this automatically, it is easy to forget that several systems are working together every time a request enters the application.
The difficulty begins when one of those systems stops working. A user logs in successfully but is immediately redirected back to the login page. A form that worked yesterday suddenly returns a 419 Page Expired error. Session data disappears after a redirect. Authentication works locally but fails after deployment. Changing the session driver creates unexpected behavior. At that point, developers often start changing .env values, clearing caches, regenerating keys, or modifying middleware without understanding which part of the request is actually failing.
The better way to troubleshoot these problems is to understand the complete journey of a Laravel session. Sessions are connected to HTTP requests, browser cookies, session identifiers, server-side storage, middleware, CSRF protection, authentication, environment configuration, and application domains. Once these pieces are seen as one system, many Laravel session errors stop looking like unrelated problems.
This guide explains that system from the browser to Laravel and back again, while also examining the most common reasons sessions expire, authentication disappears, CSRF validation fails, and users become trapped in login loops.
Understanding Why Laravel Needs Sessions
HTTP is fundamentally stateless. When a browser sends one request to a web server and then sends another request a few seconds later, HTTP does not automatically provide the application with a complete memory of what happened during the previous request.
Imagine that a user opens a login page and submits their email address and password. Laravel receives the request, verifies the credentials, and determines that the user is legitimate. The browser then requests /dashboard. Without some mechanism for maintaining state between those requests, the application would need to authenticate the user again.
Sessions solve this problem by allowing Laravel to associate information with a particular browser across multiple requests.
Laravel can use sessions for authentication information, flash messages, validation errors, temporary application state, shopping-cart information, multi-step forms, and many other features. This is why a session problem can appear to affect completely different areas of an application. The visible symptoms may be different, while the underlying problem is the same: Laravel cannot correctly connect the current request to the session it expects.
To understand why this happens, we first need to follow the request from the browser.
The Request Begins With HTTP
Suppose a user visits:
https://example.com/login
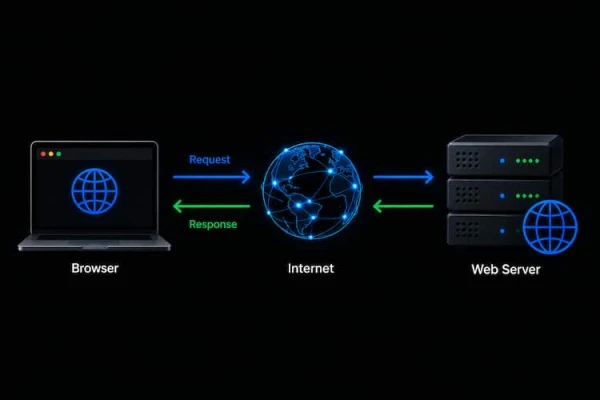
The browser sends an HTTP request to the server. Laravel receives that request and processes it through its application lifecycle. Routing determines where the request should go, middleware can inspect or modify it, and eventually the appropriate controller or application logic handles it.
When sessions are involved, Laravel needs a way to determine which session belongs to this particular browser.
That is where cookies become important.
A common misunderstanding is that the entire Laravel session is necessarily stored inside the browser cookie. In the normal session model, the cookie acts as part of the connection between the browser and the session Laravel manages. The application can then retrieve the appropriate session data using its configured session system.
This distinction becomes important during debugging. If the browser does not send the expected cookie, Laravel may not be able to continue the expected session even when the session data exists somewhere on the server.
Cookies and the Laravel Session ID
When Laravel creates a session, the browser receives a session cookie. On later requests, the browser sends the relevant cookie back according to the cookie's rules.
Laravel can then associate the request with the appropriate session.
Conceptually, the process looks like this:
Browser → Cookie → Laravel → Session → Application state
If that chain is interrupted, session behavior can break.
For example, the browser may reject the cookie. The cookie may belong to a different domain. HTTPS-related configuration may prevent it from being sent as expected. The session may no longer exist in storage. The application configuration may have changed. Or the session may have expired.
This explains why repeatedly changing authentication code is often ineffective when the real problem is cookie or session configuration.
When troubleshooting a Laravel session problem, therefore, one useful question is not simply, “Why did Laravel forget my user?” A better question is, “Did this request arrive with the information Laravel needs to find the same session?”
That question immediately creates a more systematic debugging path.
Where Laravel Stores Session Data
Laravel supports different session drivers. Depending on the application configuration, session information can be stored using mechanisms such as files, a database, Redis, or other supported storage systems.
The important point is that the browser, Laravel configuration, and session storage must work together consistently.
Consider a file-based session configuration. Laravel needs permission to write and read the appropriate session files. If filesystem permissions prevent the application from accessing them, sessions may behave unexpectedly.
A database session driver introduces different requirements. The required database structure must exist, the database connection must work, and the application must be able to read and write the session records.
Redis introduces its own infrastructure and connectivity requirements.
This is one reason a Laravel application can work perfectly on a development computer and then experience session problems after deployment. The PHP code may be identical while the environment is completely different.
If your application behaves correctly locally but changes after deployment, the problem may be broader than sessions alone. I explore that situation separately in Laravel Works Locally but Not on Server — The Hidden Differences You Must Understand.
How Session Expiration Actually Appears
A Laravel session is not intended to exist forever. Applications configure session lifetime behavior, and eventually an inactive or expired session can no longer represent the previous state in the way the user expects.
From the user's perspective, expiration can appear in several ways. They may suddenly be treated as logged out, a long-open form may fail when submitted, temporary data may disappear, or the application may redirect them somewhere unexpected.
The important lesson is that “session expired” describes an outcome, not necessarily a single cause.
A session can appear lost because it genuinely expired. But similar symptoms can happen when the browser stops sending the correct cookie, when the domain changes, when application configuration is stale, when storage fails, or when multiple environments do not share session state correctly.
This is why increasing the session lifetime should not be the automatic solution to every session-related problem. If the session disappears immediately after login, for example, a normal lifetime setting is unlikely to explain the behavior. The failure is probably occurring somewhere else in the session lifecycle.
Why Laravel Returns a 419 Page Expired Error
One of the most recognizable Laravel problems connected with sessions is the 419 Page Expired response.
Developers frequently encounter it when submitting forms. The first instinct may be to assume that the page literally became too old, but Laravel's CSRF protection is often the more useful place to investigate.
Laravel protects state-changing web requests against Cross-Site Request Forgery. Forms normally include a CSRF token, and Laravel validates that token when processing protected requests.
In a Blade form, this is commonly represented through Laravel's CSRF functionality. The important concept is not merely the syntax used to generate the token; it is the relationship between the submitted token and the user's session.
If the token expected by the application and the session state no longer correspond, validation can fail.
That is why session problems and 419 errors frequently appear together. The visible problem may be “Page Expired,” while the deeper issue involves the session that Laravel uses during CSRF validation.
If you need a focused troubleshooting guide specifically for this error, keep How to Fix the 419 Page Expired Error in Laravel as a separate article. This main guide explains the underlying session system, while the 419 article can concentrate on diagnosing that particular error.
CSRF Protection Is Part of a Larger System
It is tempting to solve every CSRF problem by checking whether the form contains the required token. That is an important check, but it is not the whole story.
Imagine that the form contains the correct CSRF field when the page is rendered. The user submits it, but the browser does not send the expected session cookie. Laravel receives the token but cannot associate the request with the expected session state. From the developer's perspective, the form looks correct, yet validation still fails.
This is why debugging should follow the complete request rather than one line of Blade code.
Check whether the form uses the correct HTTP method. Confirm that the request reaches the intended route. Determine whether the expected cookie exists in the browser. Review the session and cookie configuration. Check whether the application is switching between domains or protocols. Confirm that the session storage mechanism is functioning.
The goal is to identify where the relationship between the browser and Laravel stops being consistent.
Authentication Depends on Session Continuity
Authentication and sessions are closely related in traditional Laravel web applications.
After a successful login, the application needs to recognize the authenticated user on later requests. If session continuity fails, the credentials can be correct and the login logic can succeed while the next request still behaves as though the user were unauthenticated.
This creates one of the most confusing Laravel symptoms: the login loop.
The user enters correct credentials, submits the form, and appears to log in. Laravel redirects them to a protected page, but they are immediately returned to the login page.
At first, this looks like an authentication failure. But if credential verification succeeded, the more important question is what happened between the login request and the redirected request.
Was the session written successfully? Did the browser receive the expected cookie? Did it send that cookie on the next request? Is the protected route using the expected authentication guard and middleware? Did configuration change between requests?
This is why a login problem should not automatically be treated as a password or database problem.
For troubleshooting focused specifically on authentication behavior, Laravel Login Not Working? Session, CSRF & Redirect Fix Guide can remain a specialized guide while this article explains why sessions influence authentication in the first place.
Why APP_URL and Domain Configuration Matter
Domain configuration is another area that can create confusing session behavior.
A browser decides when to send cookies according to properties associated with those cookies. If the application is accessed through different domains or subdomains, or if environment configuration does not match the actual production environment, the browser may not behave the way the developer expects.
For example, development might happen at a local address while production uses HTTPS on a real domain. A staging environment may use a subdomain. An application might be moved behind a proxy or configured differently after deployment.
This does not mean that changing APP_URL magically fixes every session problem. Instead, it means that the application's URL, cookie domain, secure-cookie behavior, environment, and actual way users access the site should be considered together.
A configuration value copied from another environment can create problems even when the application code itself is correct.
Why .env Changes Sometimes Seem to Do Nothing
Laravel developers often modify .env, refresh the browser, and become confused when nothing changes.
The reason may be cached configuration.
Laravel is designed to optimize configuration handling, particularly in production. Once configuration has been cached, editing .env does not necessarily mean the running application will immediately behave according to the new value.
This becomes especially confusing during session troubleshooting because developers may change the session driver, lifetime, domain, or another related setting and assume the change has been applied.
Before making additional changes, confirm what configuration the application is actually using.
I cover this problem in more detail in Laravel .env Not Working? Fix Config Cache Problems, because configuration caching affects much more than sessions.
The larger lesson is simple: never debug only the configuration you intended Laravel to use. Debug the configuration Laravel is actually running with.
Session Drivers Can Fail in Different Ways
Changing the session driver can solve a legitimate infrastructure problem, but it should not become a random troubleshooting technique.
Each driver has requirements.
With file sessions, storage access and permissions matter. With database sessions, database availability and the expected session table matter. With Redis, connectivity and Redis configuration matter. In distributed environments, session architecture becomes even more important because requests may be processed by different application instances.
This is why changing from one driver to another without understanding the cause can hide the original problem or create a new one.
Instead, begin with the current driver and verify its complete path. Can Laravel write the session? Can it read it on the next request? Does the session persist for the expected amount of time? Is the browser consistently providing the session identifier?
This approach produces evidence instead of guesses.
File Permissions and Session Problems
File permissions deserve particular attention on deployed Laravel applications.
Laravel needs write access to specific application directories for features such as logs, cache files, compiled views, and file-based sessions. Incorrect ownership or permissions can therefore create problems that appear unrelated at first.
A session that cannot be written correctly can lead to authentication loss. A cache problem can make configuration changes appear ineffective. A logging problem can make troubleshooting harder because useful error information never reaches the expected log.
The correct permission setup depends on the server environment, so copying an arbitrary permission command from the internet is not always the best solution. The goal is to understand which user runs PHP or the web server, which directories Laravel needs to write to, and whether ownership and permissions allow that access without unnecessarily exposing the application.
This is a good example of why deployment knowledge matters even when the visible error appears inside Laravel.
A Better Way to Debug Laravel Session Problems
When a session breaks, changing five configuration values at once makes troubleshooting harder because you no longer know which change affected the result. A more reliable approach is to follow the session lifecycle in order.
Start with the browser. Determine whether the expected cookie exists and whether it is being sent with the request. Then examine Laravel's environment and cookie configuration. Confirm the session driver and verify that its storage mechanism works. Check whether configuration caching means Laravel is using older values. Follow the request through middleware and authentication. If CSRF validation is involved, verify the relationship between the form token and the session.
Then reproduce the problem carefully.
Suppose authentication disappears after a redirect. That gives you a boundary: something changed between the login request and the next request. Instead of investigating the entire application, compare those two requests.
Suppose the application works locally but fails only in production. That gives you another boundary: investigate environmental differences rather than rewriting working application logic.
Good debugging is often the process of making the problem smaller.
This same principle is useful beyond sessions, which is why a broader debugging methodology belongs in a separate Laravel debugging guide rather than repeating every possible session fix here.
Common Mistakes When Fixing Laravel Sessions
One of the biggest mistakes is assuming every session problem has the same solution. Developers see a 419 response and immediately clear every cache. They see a login loop and regenerate APP_KEY. They see disappearing session data and switch drivers. Sometimes the application starts working afterward, but that does not necessarily mean the underlying cause was understood.
Another mistake is changing production configuration without recording the previous state. If several values are changed together, diagnosing the original problem becomes difficult and reverting safely becomes harder.
Developers can also focus too heavily on Laravel while ignoring the browser. Cookies are controlled partly by browser rules, and the browser's developer tools can reveal whether the expected cookie exists, which domain it belongs to, whether it is secure, and whether requests actually include it.
Finally, do not ignore infrastructure. PHP configuration, server permissions, HTTPS, proxies, load balancing, Redis, database availability, and deployment configuration can all influence behavior that eventually appears as a Laravel session error.
Preventing Session Problems Before They Reach Production
The best session problem is the one users never encounter.
Production configuration should be deliberate rather than copied blindly from development. The application should use the correct environment values, secure settings appropriate to HTTPS, a session driver suitable for its architecture, and permissions that allow Laravel to perform required operations safely.
Deployment procedures should also account for Laravel's caches. When configuration changes, the deployment process should ensure that the running application receives the intended configuration.
Testing should include more than opening the homepage. Authentication flows, form submissions, redirects, validation errors, logout behavior, long-running forms, and protected routes are all useful places to test session continuity.
Logging and monitoring also matter. If session-related behavior begins failing after a deployment, knowing exactly what changed can dramatically reduce debugging time.
Most importantly, developers should understand the architecture before an error occurs. Knowing how browser cookies, session storage, Laravel middleware, CSRF protection, and authentication fit together makes troubleshooting much faster when something eventually fails.
Understanding the Complete Laravel Session Lifecycle
The easiest way to remember Laravel sessions is to stop thinking of them as one isolated framework feature.
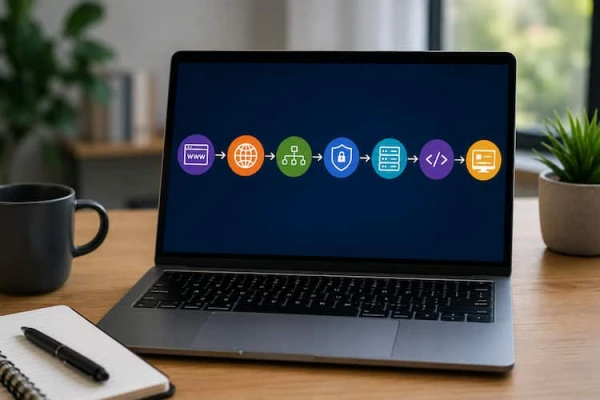
A browser sends an HTTP request. Cookies help Laravel associate that request with an existing session. Laravel reads session information from the configured storage mechanism. Middleware makes that state available during request processing. CSRF protection can use session-related state to validate protected requests. Authentication can rely on session continuity to recognize a user across requests. Laravel eventually creates a response, and the browser continues the cycle on the next request.
The important chain is:
HTTP request → Cookie → Session ID → Session storage → Middleware → CSRF/Authentication → Response → Next request
A failure anywhere in that chain can produce a symptom somewhere else.
A cookie problem can look like an authentication problem. A session-storage problem can look like a CSRF problem. Cached configuration can look like a broken .env file. Incorrect deployment settings can make perfectly valid Laravel code appear defective.
Understanding these relationships is much more useful than memorizing a list of commands.
Conclusion
Laravel sessions become difficult to troubleshoot when we see only the final error. A 419 response, an expired session, disappearing authentication, or a login loop may look like separate problems, but they often involve the same underlying journey between the browser and the application.
The browser must send the appropriate information. Laravel must identify the correct session. The configured session driver must store and retrieve state correctly. Cookie and domain settings must match the environment. Middleware must process the request as expected. CSRF protection must be able to validate the request, and authentication must be able to continue the user's identity across requests.
Once this lifecycle is understood, debugging becomes much more systematic. Instead of randomly clearing caches or changing configuration, you can ask where the expected state disappeared and investigate that specific part of the request.
That is the real value of understanding Laravel sessions. The goal is not simply to fix one Laravel session expired error or one 419 Page Expired response. It is to understand the architecture well enough that when a session, cookie, CSRF token, or authentication flow fails, you know where to begin looking.
Discussion 0